From regulated requirement to accepted release.
We turn attack surface into defensible assurance. SPNORTH Security/Research tests, hardens and evidences – PTaaS, NIS2 and ISO 27001 with an evidence chain and human accountability.
Synthetic illustration: abstract sketch with sample data; no customer system. 19+ years founder experience in regulated IT delivery (source: CV/catalogue §1) ISO 27001 ISMS Manager & Auditor, TÜV Austria 2025 (source: catalogue §1) 4 paths solution paths for delivery, regulation, data, AI 10–15 min free fit evaluation, human, no obligation Common triggers – direct entry SPNORTH Consulting
External attack surface grows with every release; web apps, APIs and cloud configuration are tested only episodically. Consequence: vulnerabilities live for months, prioritization follows gut feeling instead of CVSS, and evidence is missing.
Attack surface: penetration tests & PTaaS SPNORTH Consulting
NIS2 and ISO 27001 requirements sit scattered across documents; ownership, controls and evidence are unclear. Consequence: audits expose gaps, management liability stays untreated and the deadline runs.
NIS2 & regulation into practice SPNORTH Consulting
Scanner reports pile up without prioritization; no owner, no SLA, no traceable remediation loop. Consequence: risks are reported but not removed — and management only sees noise.
Vulnerability management with evidence SPNORTH Consulting
AI agents read sensor data and touch systems; prompt injection, data exfiltration and missing logs go untreated. Consequence: an incident via the agent is not demonstrably covered — liability and notification risk.
Security in AI operations Two lines, one accountability Test, harden, prove — a accountable path from attack surface to defensible assurance.
You get: a solid decision with basis, options and next step – not an endless workshop carousel.
Operate services are an optional continuation after delivery – not a separate top-level line.
How engagement works Free fit evaluation (10–15 min) – problem, fit, next step. Paid diagnostic, if qualified – scope and commercial terms only here. SPNORTH Security ansehen delivers – with approvals and evidence. Operate services optionally, where recurring value and an exit path exist. Synthetic illustration: abstract sketch with sample data; no customer system. Three entry levels (scope, not packages) Focused start - One decision, workflow, interface or release problem.Team delivery - One product, programme or bounded engineering workstream.Multi-stream transformation - Several interdependent teams, systems or control domains.Products Status: proposed
A scheduled, repeating penetration-testing programme with scope rhythm, retests and assessment evidence.
Status: proposed
A structured control framework for NIS2 readiness: roles, risks, notification paths and evidence at a glance.
Status: proposed
From finding to retest: a logged vulnerability workflow with owner, SLA and tamper-evident records.
Status: proposed
A ready-made baseline of policies, checklists and training templates for visible basic hygiene from day one.
Proof, not claims Evidence accrues visibly: synthetic demos, expert review, pilot metrics with baseline, permissioned customer voices – in that order. See the methodology
Who is behind this Founded by a senior practitioner: 19+ years of project, product and transformation leadership in banking, insurance, telecom and critical infrastructure; ISMS Manager & Auditor ISO 27001 (TÜV Austria); certified Compliance Officer (ARS Academy).
See profile and governance
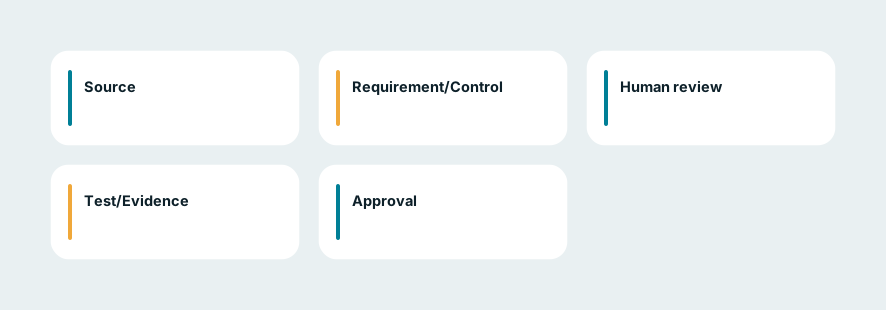
Evidence Flow Synthetic example Synthetic example: illustrated demo with sample data; no customer system and no live telemetry.
1 Source Approved source with version and rights (sample dataset)
2 Requirement/Control Derived requirement with control target and owner
3 Human Review Named approver reviews context, conflicts and evidence
4 Test/Evidence Evaluation against ground truth; reproducible result
5 Approval Signed decision with date and evidence index
Delivery lifecycle in detail ->
Ready for the free fit evaluation? 10–15 minutes, free and no obligation – fit, ownership and the next step instead of free consulting.
Free fit evaluation